What You Need to Know About Salesforce Security Risks (Podcast)
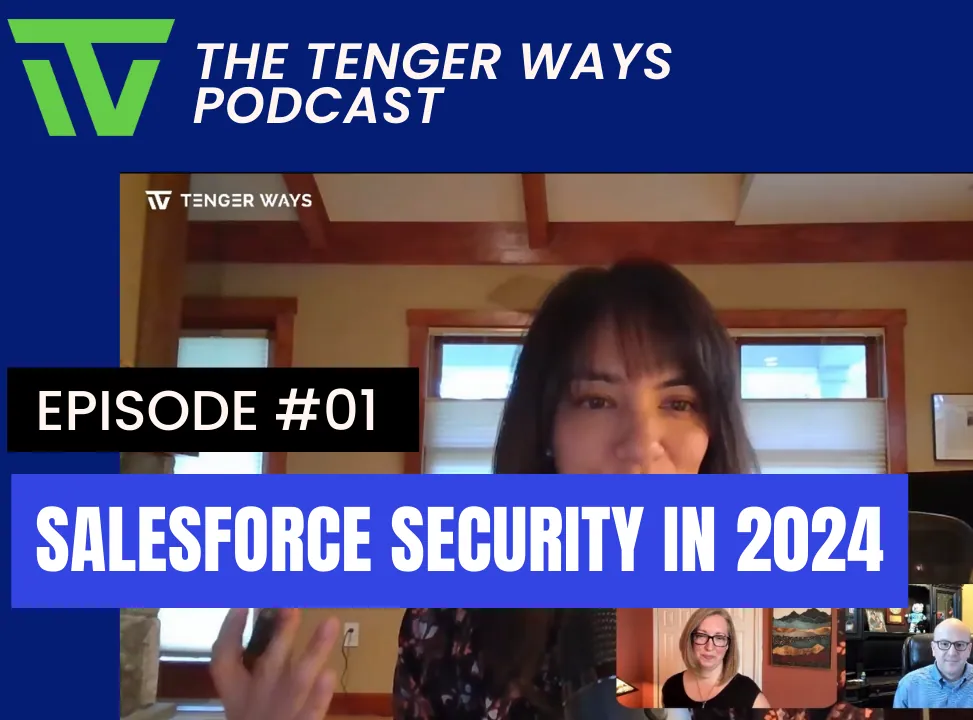
Tenger Ways cofounders Adrienne Shulman and Daniel Keith sit down with Salesforce Practice Lead Sandi Nuss Zellner to talk about Salesforce and Security - watch the podcast to learn everything you need to know in 2024 to protect the sensitive and critical data in your Salesforce application.
By Adrienne Shulman · 1 min read
 Expand image
In our recent 3 part blog series we explored everything you need to know about securing the very sensitive and critical data in your Salesforce application. Read about Installed Packages in part 1, Custom Code in part 2, and Profiles and Permission Sets in part 3. In addition, Tenger Ways cofounders Adrienne Shulman and Daniel Keith sat down with Salesforce Practice Lead, Sandi Nuss Zellner, to discuss these topics in a deeper conversation on our podcast.
In our 50 minute conversation we covered:
- Big picture themes related to Salesforce and security, answering the question, “what does security mean in the context of a cloud, SaaS application?” and dispelled the myth that security is handled by cloud vendors.
- Installed packages - what they are, the security risks they present, and what you need to be thinking about and doing today to mitigate the risks.
- Custom Code - what they are, the security risks they present, and what you need to be thinking about and doing today to mitigate the risks.
- Profiles and Permission Sets - what they are, the security risks they present, and what you need to be thinking about and doing today to mitigate the risks.
You can watch the podcast right here on our website, or find it on Spotify, YouTube or Apple Podcasts (audio only).
Let us know what you think of the episode and any other questions you have about Salesforce or Security.